Unknown Exposure
Firewalls, endpoints, cloud accounts, and user access can all drift away from their intended security posture over time. Penetration testing gives your team a clearer view of which weaknesses could be used in a real attack path.
Penetration testing from Northern Hills Technology helps uncover exploitable weaknesses before they become business disruptions, compliance concerns, or costly security incidents. For organizations in Spearfish, Rapid City, Sturgis, Belle Fourche, Gillette, and the broader Black Hills region, our testing connects technical findings to practical risk, remediation priorities, and long-term cybersecurity planning. We help regulated and security-conscious teams understand where their defenses stand without overstating what any single test can guarantee.
The goal is not to overwhelm your team with technical noise. The goal is to validate defenses, clarify risk, and help you decide what to fix first.
Test how weaknesses could be combined and exploited in a real attack.
Translate findings into clear severity, impact, and remediation priorities.
Use test results to support broader security and compliance discussions.
Turn testing results into ongoing monitoring, remediation, and protection improvements.
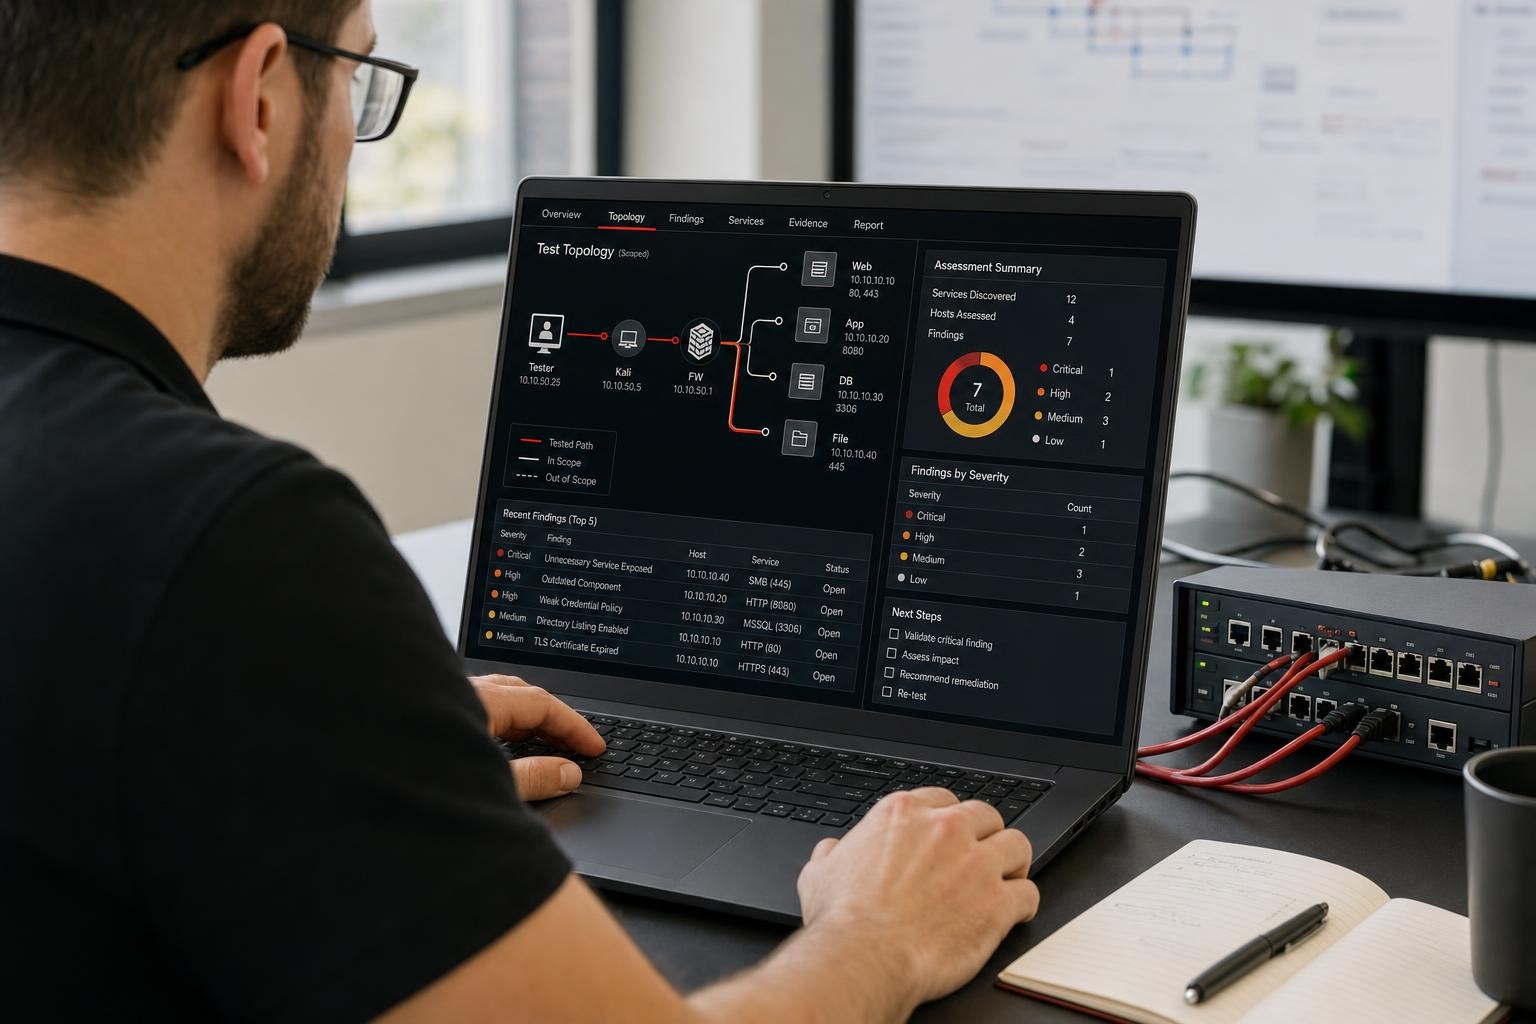
A penetration test typically evaluates selected systems, networks, applications, users, or environments based on the agreed scope. The process may include discovery, controlled testing, evidence collection, risk ranking, and a report with remediation recommendations. Northern Hills Technology defines scope before testing begins so your team understands what will be assessed and what is outside the engagement.
Vulnerability scanning identifies known weaknesses, misconfigurations, and missing updates across selected assets. Penetration testing goes further by validating whether weaknesses may be exploitable in a realistic attack scenario. Both are useful, and Northern Hills Technology can help determine how scanning and testing should work together in your security program.
Testing is planned to reduce unnecessary disruption, but any security test carries some operational consideration. Before work begins, Northern Hills Technology reviews scope, timing, communication paths, and any sensitive systems that need special handling. The intent is to gather meaningful security evidence while respecting your organization’s operational requirements.
Many regulated or security-conscious organizations use penetration testing to support risk management, insurance discussions, internal governance, and compliance alignment. Requirements vary by industry, framework, contract, and regulator, so testing should be matched to your specific obligations. Northern Hills Technology works with organizations navigating frameworks such as HIPAA, NIST, FTC Safeguards, PCI-DSS, and CIS.
The right schedule depends on your risk profile, regulatory environment, infrastructure changes, and business priorities. Many organizations test annually, after major technology changes, or when preparing for a compliance or insurance review. Northern Hills Technology can help build testing into a broader cybersecurity plan that also includes vulnerability management and monitoring.
You receive findings that explain what was tested, what was discovered, how risks are prioritized, and what remediation steps should be considered. Northern Hills Technology can review results with leadership and technical stakeholders so the next steps are clear. When appropriate, findings can be connected to managed IT, cybersecurity, compliance, backup, and long-term technology planning.
Keep your business running smoothly with proactive monitoring, responsive IT support, and ongoing system maintenance. From Spearfish, we help Black Hills organizations reduce downtime, manage technology upgrades, and plan ahead—all through one accountable IT partner.
Northern Hills Technology provides cybersecurity services for organizations that need stronger protection without adding the overhead of an internal security department. From Spearfish and the Greater Black Hills region, our MSP/MSSP approach combines 24/7 monitoring and remediation, endpoint protection, vulnerability management, and practical security leadership for regulated and security-conscious businesses. We help leaders address ransomware risk, insurance pressure, compliance requirements, and everyday security gaps with clear communication and a predictable monthly service model.
Align your technology with frameworks such as HIPAA, NIST, PCI-DSS, CIS, CJIS, GDPR, and FTC Safeguards through practical security, documentation, training, and reporting.